
GRC Analyst Accelerator
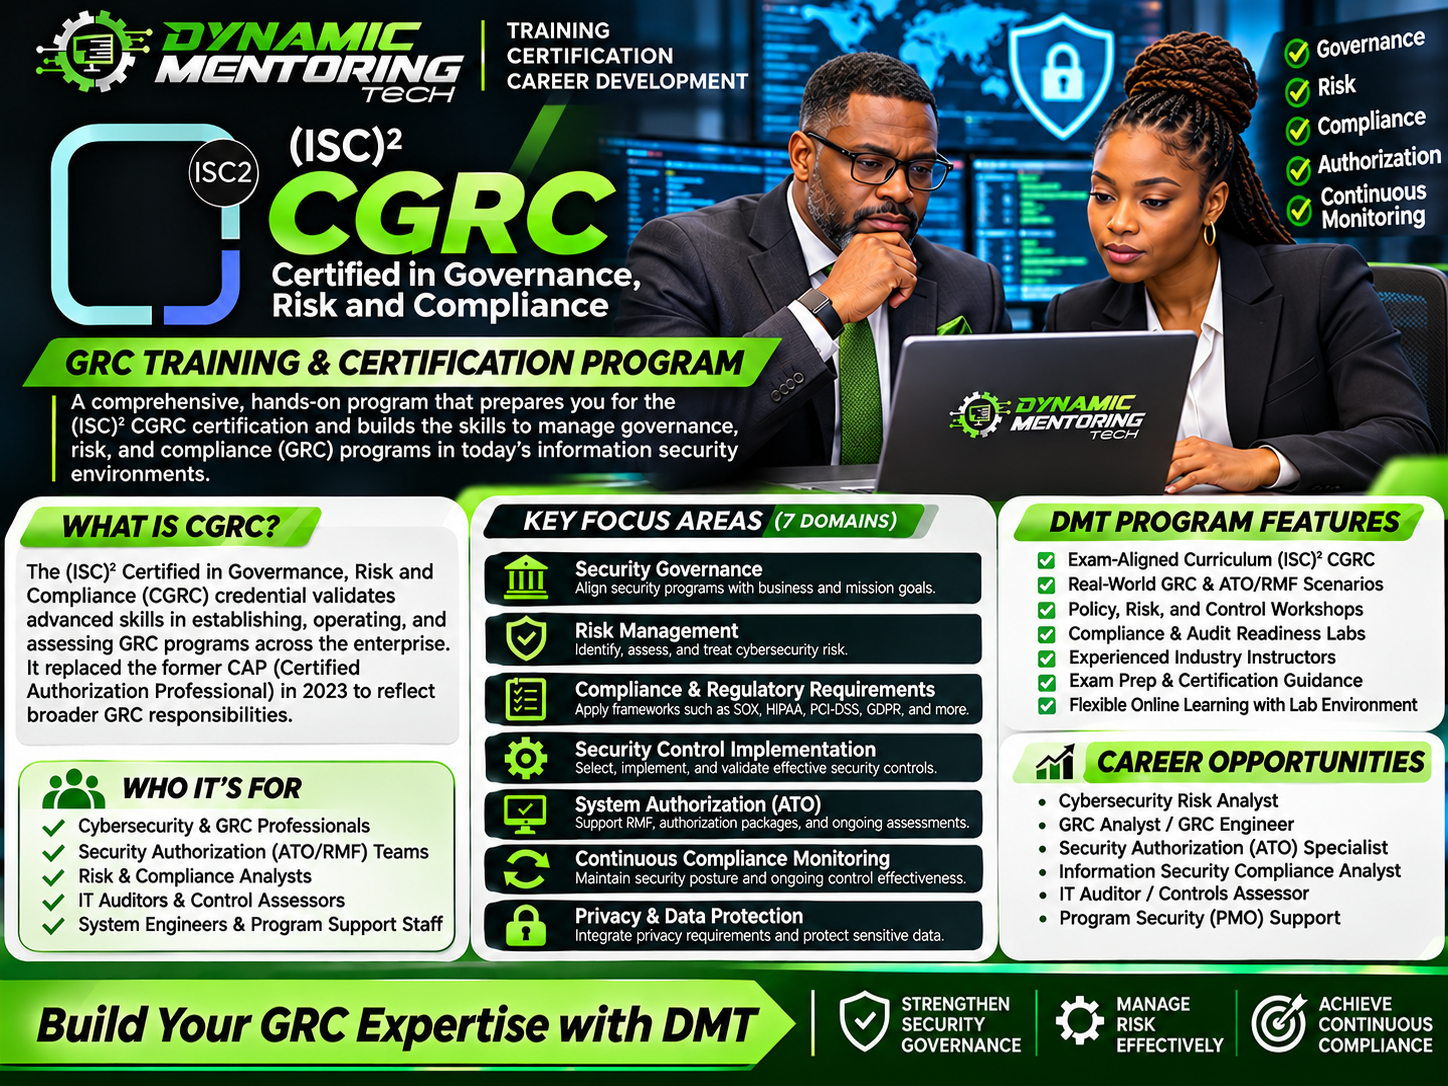
ISC2 CGRC – Governance, Risk & Compliance Training and Certification Program
Build Your GRC Expertise. Strengthen Cybersecurity. Advance Your Career.
Take your cybersecurity career to the next level with Dynamic Mentoring Tech (DMT)!
In today’s rapidly evolving cybersecurity landscape, organizations need skilled professionals who can effectively manage security governance, assess cybersecurity risks, maintain regulatory compliance, and support secure information systems. Dynamic Mentoring Tech’s ISC2 Certified in Governance, Risk and Compliance (CGRC) Training and Certification Program is designed to equip aspiring and experienced cybersecurity professionals with the technical knowledge, practical experience, and industry-aligned skills needed to succeed in Governance, Risk, and Compliance (GRC).
Our comprehensive, hands-on training program goes beyond traditional certification preparation. Students develop practical skills in Risk Management Framework (RMF), Authority to Operate (ATO), security control implementation, risk assessments, compliance auditing, continuous monitoring, and security authorization processes.
Through real-world scenarios, interactive workshops, and practical lab exercises, participants learn how to evaluate cybersecurity risks, implement security controls, develop authorization documentation, and support enterprise security compliance initiatives across government and commercial environments.
What Makes the DMT CGRC Program Different?
At Dynamic Mentoring Tech, we believe that certifications validate knowledge, but hands-on experience builds careers.
Our program emphasizes practical applications of governance, risk, and compliance principles, including:
- Governance & Risk Management: Develop cybersecurity governance strategies, assess organizational risks, and align security programs with business objectives.
- NIST RMF & ATO Operations: Gain practical exposure to system categorization, security control selection, implementation, assessment, authorization, and continuous monitoring.
- Security Compliance & Auditing: Explore regulatory and security frameworks, including NIST SP 800-53, FISMA, HIPAA, PCI DSS, and other applicable requirements.
- Security Authorization Documentation: Learn how to support System Security Plans (SSPs), Plans of Action and Milestones (POA&Ms), risk assessments, and authorization packages.
- Continuous Monitoring & Vulnerability Management: Understand security posture management, remediation tracking, compliance reporting, and ongoing authorization responsibilities.
- Certification Preparation: Build the knowledge and confidence needed to prepare for the ISC2 CGRC certification examination.
Program Outcomes: What You Will Be Able to Do
From understanding cybersecurity compliance to performing real-world GRC operations.
Upon successful completion of the DMT CGRC Training and Certification Program, students will be prepared to demonstrate the following practical competencies:
- Apply the NIST Risk Management Framework (RMF): Perform the seven RMF steps—Prepare, Categorize, Select, Implement, Assess, Authorize, and Monitor—within simulated enterprise and federal cybersecurity environments.
- Support Authority to Operate (ATO) Processes: Develop and maintain security authorization documentation, track authorization conditions, and support ongoing system compliance requirements.
- Conduct Cybersecurity Risk Assessments: Identify threats, vulnerabilities, and security weaknesses; evaluate organizational risk; and recommend appropriate mitigation strategies.
- Implement and Assess Security Controls: Apply NIST SP 800-53 security controls, evaluate control effectiveness, identify deficiencies, and document corrective actions.
- Develop Security Compliance Documentation: Create sample System Security Plans (SSPs), Plans of Action and Milestones (POA&Ms), risk assessment reports, and security control assessment documentation.
- Perform Vulnerability and Compliance Management: Interpret vulnerability assessment findings, prioritize remediation activities, track security weaknesses, and support continuous monitoring using simulated enterprise security data.
- Support Security Audits and Regulatory Compliance: Evaluate systems against applicable security requirements, organize audit evidence, and communicate compliance findings to stakeholders.
- Communicate Cybersecurity Risk to Leadership: Prepare risk summaries, compliance scorecards, executive briefings, and recommendations that support informed security decisions.
- Build a Professional GRC Project Portfolio: Demonstrate practical competencies through documented security assessments, risk registers, authorization artifacts, and a comprehensive GRC capstone project.
- Prepare for the ISC2 CGRC Certification Examination: Develop knowledge across the official CGRC exam domains and strengthen readiness through exam-aligned instruction, practice questions, and review exercises.
Student Capstone: Build a Real-World GRC Authorization Package
As a culminating project, students will develop a simulated Governance, Risk, and Compliance Security Authorization Portfolio for an enterprise information system.
The portfolio will include:
- System categorization and security boundary documentation
- Security control selection and implementation matrix
- System Security Plan (SSP)
- Cybersecurity Risk Assessment Report
- Security Assessment Report (SAR)
- Plan of Action and Milestones (POA&M)
- Continuous Monitoring Strategy
- ATO readiness briefing and executive risk summary
The Result: Students complete the program with practical GRC work samples that can be presented and discussed during cybersecurity job interviews, demonstrating their ability to apply security governance, risk management, and compliance principles.
Prepare for High-Demand Cybersecurity Careers
The DMT CGRC program supports career development for professionals pursuing roles such as:
- Cybersecurity Risk Analyst
- Governance, Risk & Compliance (GRC) Analyst
- GRC Engineer
- Information System Security Officer (ISSO)
- Security Control Assessor (SCA)
- Security Authorization / ATO Specialist
- Cybersecurity Compliance Analyst
- IT Auditor and Risk Management Specialist
Whether you are transitioning into cybersecurity, expanding your existing technical expertise, or preparing for responsibilities within federal cybersecurity programs, DMT provides a practical pathway toward professional growth.
Your Future in Cybersecurity Governance Starts Here!
Dynamic Mentoring Tech is committed to developing career-ready cybersecurity professionals through technical education, industry-recognized certification preparation, and practical workforce development.
Don’t just learn compliance requirements. Learn how to implement, assess, manage, and maintain them in real-world cybersecurity environments.
Train with DMT. Build Real Skills. Earn Industry-Recognized Credentials. Advance Your Career.
Dynamic Mentoring Tech
Website: https://dynamicmentoring.org
Email: info@dynamicmentoring.org
Phone: 240-695-6564
Certification is awarded by ISC2 upon satisfying its examination, experience, and other applicable requirements. DMT provides training and certification preparation; successful completion of training does not guarantee certification.